home  /  about
the institute

Why this institute exists.

Who runs it, how it is paid, what it will and will not tell you, and why it sells no security of its own.

talk to the Institute
mission

Almost everyone who will tell you whether your security was reasonable also sells security.

After an incident an organization is surrounded by opinions from parties with a stake in the answer: the responder who wants the engagement, the vendor whose product would have helped, the insurer deciding coverage, and opposing counsel. A disinterested read on what the safeguards actually were, measured against what they should have been, is the one thing rarely available.

The Cybersecurity Incident Institute exists to supply that read, and to make the first hour of it free. Anyone can use the Institute’s concierge at no charge: it asks what happened and when it was found, says plainly what evidence is disappearing and how fast, explains what a standard-of-care analysis would examine, and identifies what kind of expertise the matter actually needs.

The reference material covers three areas, in the order a matter moves through them. Whether the security was reasonable for the risk the organization actually carried. Whether the response, judged on what was known at each moment, was adequate. And whether the failure caused the exposure, which is a longer chain than either side usually argues.

What the Institute does not do is sell security. No incident response, no products, no managed services, no assessments that conclude by recommending a purchase. That is not modesty about scope, it is the condition that makes the analysis worth anything.

plainly stated

What the Institute is and is not.

The Institute is

  • A knowledge institution. Plain-language references on the standard of care, response adequacy, forensics and technical causation, written for the people who have to decide quickly.
  • Independent of every vendor. The Institute sells no security products, no incident response and no managed services, and takes no money from anyone who does.
  • Neutral as to side. It serves plaintiff and defense counsel, insurers and insureds, boards and regulators, matter by matter. The technical facts do not change according to who asked.
  • Free at the point of use. The concierge, the references and the preservation guidance cost nothing and require no account.

The Institute is not

  • Not an incident response firm. It does not respond to live incidents, contain intrusions or perform remediation. If you are mid-incident you need a responder, and the Institute will say so rather than take the work.
  • Not a security opinion. Nothing here concludes that a particular organization’s security was or was not reasonable. Naming what an analysis requires is not the same as performing it.
  • Not legal advice. Whether a duty existed, what notification obligations apply and on what clock, and whether exposure alone is a cognisable injury are questions of law that vary by jurisdiction. Those belong to counsel.
  • Not a party to your matter. Using this site creates no attorney-client or expert relationship, and concierge conversations are neither privileged nor confidential. Do not put incident detail, privileged material or client identities into it.

How the Institute sustains itself

The orientation and the reference material are free and stay free. Where an organization wants the standard-of-care review performed properly, independently, and ideally before anyone is demanding it under oath, that is a private engagement billed as a fixed fee agreed in writing before any work begins.

Where a matter requires a retained testifying expert, for a standard-of-care opinion, a forensic analysis or a response-adequacy review, the Institute arranges the engagement through its expert network and is compensated for that work.

The Institute sells no security products, no incident response and no managed services, and accepts no compensation from any company that does. No sponsorship, no referral fee, no affiliate arrangement, no paid placement. That matters more here than in most fields: an assessment of whether security was adequate, produced by someone who also sells the security, is worth very little, and everyone in this market knows it.

We publish this because the people reading it cross-examine for a living or decide coverage for a living, and should not have to guess.

leadership

Leadership.

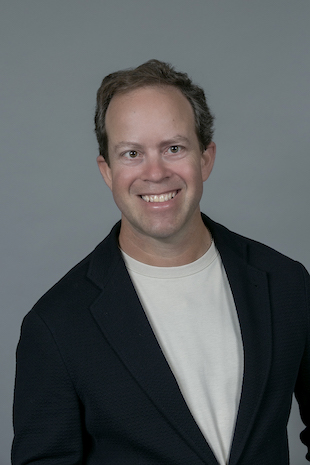
Russ Rosenzweig, Executive Director of the Cybersecurity Incident Institute
Announcement · September 2026

Russ Rosenzweig named Executive Director of the Institute

Russ Rosenzweig was named Executive Director of the Cybersecurity Incident Institute in September 2026. He was one of the pioneers of the expert witness industry and has decades of experience helping clients understand complex technical disputes and connecting them with the right experts and knowledge bases.

He founded the first expert witness search and referral firm in 1993 and led it for three decades, connecting thousands of attorneys, insurers and companies with specialized experts. His clients have included most of the largest law firms in the United States.

Breach matters are a hard version of the problem he has worked on throughout that career. The right witness may be a security architect, a digital forensics examiner, a former regulator, a compliance specialist or an academic, and the wrong choice is rarely obvious until the deposition. Three decades of watching which combinations hold up under cross-examination is the relevant experience here.

B.A., Northwestern University  ·  M.B.A., University of Chicago Booth School of Business

the network

The specialists behind the answers.

Breach disputes rarely sit inside one discipline. A standard-of-care opinion needs someone who has actually run security programs at comparable organizations. Forensics needs an examiner whose methodology will survive challenge. Response adequacy needs someone who has managed real incidents under pressure rather than only written about them. Regulatory exposure may need a former regulator, and causation frequently needs an economist the Institute does not supply.

The Institute draws on a working network built over thirty years across those fields, and engages specialists matter by matter; they remain independent. Its role is to work out what the matter actually requires and then find the right person, including saying when the answer is a discipline it does not itself cover.

An advisory council of security practitioners, forensic examiners and coverage counsel is being convened and will be named here.
standards

The rules this site holds itself to.

We sell no security

No products, no incident response, no managed services, and no compensation from anyone who sells them. An adequacy opinion from a party that also sells the remedy is worth very little.

Preservation comes first

Where a visitor describes a live or recent incident, the concierge raises what is disappearing before it discusses anything else. Logs roll over in days, and that window does not reopen.

No opinion on your security

The Institute explains what a standard-of-care analysis asks and what evidence it needs. Whether a particular organization met it is the expert opinion this site helps you obtain, not the one it supplies.

Neutral as to side

Plaintiff and defense, insurer and insured, board and regulator. The technical facts do not change according to who asked, and an institution that only reached convenient conclusions would be worth consulting from neither side.

Claims with a date on them

Frameworks are revised, retention defaults change, and the legal questions here are genuinely unsettled and moving. Anything stated carries what it rests on and when.

Corrections

Errors, once known, get fixed. If something on this site is wrong, tell the Institute and it will be reviewed and corrected.

Preserve today. Analyze tomorrow.

Start free with the Incident Concierge, or talk to the Institute directly.

talk to the Institute
incident conciergeorientation · not a security opinion
Happy to explain. I can tell you what the Institute covers, how it is paid, or help you scope an incident. I won't assess a live incident, opine on whether security was reasonable, or give legal advice.